SASO Updates Smart Lock Certification: Arabic UI & Local Pen Testing Mandatory from June 2026
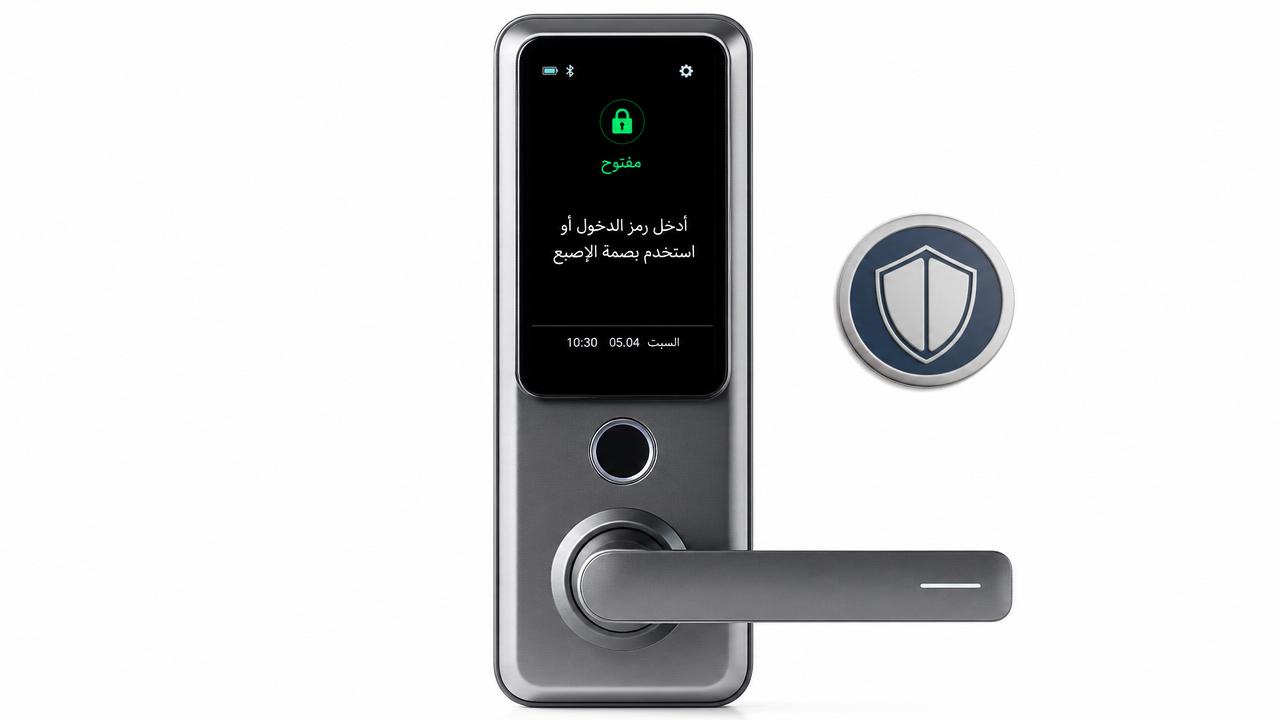
Saudi Arabia’s Standards, Metrology and Quality Organization (SASO) updated its supplementary requirements to SASO IEC 62368-1 on May 16, 2026. Effective June 1, 2026, all digital locks and smart access control systems entering the Saudi market must comply with two new mandatory requirements: full Arabic-language user interface localization and locally conducted penetration testing authorized by the National Cybersecurity Authority (NCA). This development is particularly relevant for manufacturers, exporters, cybersecurity service providers, and certification bodies engaged in the smart home security and electronic access control sectors.
Event Overview
On May 16, 2026, SASO issued an update to the supplementary clauses of SASO IEC 62368-1. The update mandates that, starting June 1, 2026, all digital locks and smart door access systems placed on the Saudi market must pass two newly introduced compliance tests: (1) verification of complete Arabic-language localization across all user-facing interfaces; and (2) penetration testing performed exclusively by NCA-accredited laboratories in Saudi Arabia, including simulated WPS brute-force attacks and BLE channel hijacking scenarios.
Industries Affected by the Update
Smart Lock Manufacturers & OEMs: These entities are directly responsible for product design, firmware implementation, and pre-market conformity assessment. Non-compliance will block market entry, as SASO certification — now including both language validation and NCA-aligned penetration testing — is a prerequisite for customs clearance and sale in Saudi Arabia.
Exporters & Importers of Access Control Systems: Companies managing cross-border shipments must verify that incoming products meet the updated technical and procedural requirements before dispatch. Failure to confirm compliance may result in shipment rejection, rework delays, or post-arrival non-conformance penalties.
Cybersecurity Testing Laboratories: Only NCA-authorized labs in Saudi Arabia may conduct the required penetration tests. International labs — even those accredited to ISO/IEC 17025 or common global standards — cannot fulfill this requirement unless formally recognized by NCA. This restricts testing options and may extend time-to-certification cycles.
Certification Bodies & Conformity Assessment Providers: Entities issuing SASO CoC (Certificate of Conformity) must now validate evidence of both Arabic UI compliance and NCA-authorized test reports. Their internal checklists and audit protocols require immediate revision to reflect these two new checkpoints.
What Relevant Enterprises or Practitioners Should Focus On — And How to Respond Now
Monitor official SASO and NCA guidance for implementation details
The May 16 update confirms the requirement but does not yet publish full test methodologies, acceptance criteria for Arabic UI (e.g., RTL rendering, dialect coverage, error message translation), or NCA’s lab accreditation list. Stakeholders should track SASO’s official portal and NCA’s published notices for finalized annexes and procedural bulletins.
Confirm whether existing product lines support full Arabic UI at firmware and hardware levels
Arabic UI compliance goes beyond simple text translation: it requires right-to-left (RTL) layout support, Unicode-compliant fonts, culturally appropriate icons, and localized error handling. Manufacturers should audit current firmware versions and assess whether UI frameworks support dynamic language switching without hardware modification.
Engage early with NCA-authorized labs for test scheduling and scope alignment
Given limited capacity at NCA-accredited facilities — especially for specialized BLE and WPS attack simulations — lead times for penetration testing are expected to increase. Companies planning market entry after June 2026 should initiate lab engagement now, sharing product architecture documents and wireless communication specifications to align on test scope and reporting format.
Distinguish between regulatory signal and operational readiness
This update is a formal regulatory amendment, not a draft proposal. While transitional arrangements (e.g., grace periods for legacy stock) have not been announced, the effective date of June 1, 2026 is binding. Businesses should treat this as an enforceable requirement — not a pending recommendation — when updating product roadmaps and compliance timelines.
Editorial Perspective / Industry Observation
Observably, this update reflects SASO’s broader shift toward integrating linguistic accessibility and nationally anchored cybersecurity assurance into technical regulation — moving beyond baseline safety (IEC 62368-1) into domain-specific usability and threat-resilience expectations. Analysis shows that the pairing of Arabic UI and local penetration testing signals a dual emphasis: user inclusivity and sovereign cyber risk management. From an industry perspective, this is less a one-off certification hurdle and more an indicator of tightening localization expectations across Saudi digital product regulations. It is currently best understood as an operational requirement already in force — not a future policy signal — requiring concrete technical and procedural adjustments prior to June 2026.
Conclusively, this SASO update establishes new, non-negotiable baselines for market access in Saudi Arabia’s smart lock and access control segment. Its significance lies not in novelty alone, but in the explicit linkage of language compliance with nationally supervised cybersecurity validation — a combination that raises both technical and logistical thresholds for global suppliers. At present, it is most appropriately interpreted as an enforceable compliance milestone demanding targeted, near-term action across R&D, testing, and certification workflows.
Source: Saudi Standards, Metrology and Quality Organization (SASO); National Cybersecurity Authority (NCA) of Saudi Arabia. Note: Specific test methodology documents, Arabic UI evaluation criteria, and the official list of NCA-accredited laboratories remain pending publication and are subject to ongoing monitoring.
Industry Briefing
Get the top 5 industry headlines delivered to your inbox every morning.