Saudi SASO Rule Sets Cybersecurity Approval for Digital Locks
On July 10, 2026, the Saudi Standards, Metrology and Quality Organization (SASO) formally issued a mandatory enforcement notice for SASO IEC 62443-3-3:2026, making cybersecurity certification a market-access requirement for imported digital locks from September 15, 2026. For exporters, manufacturers, testing teams, importers, and logistics operators serving the Saudi market, this is not simply a standards update; it directly affects product entry, testing timelines, customs preparation, and the risk of shipment rejection at Riyadh port.
What the new requirement formally changes
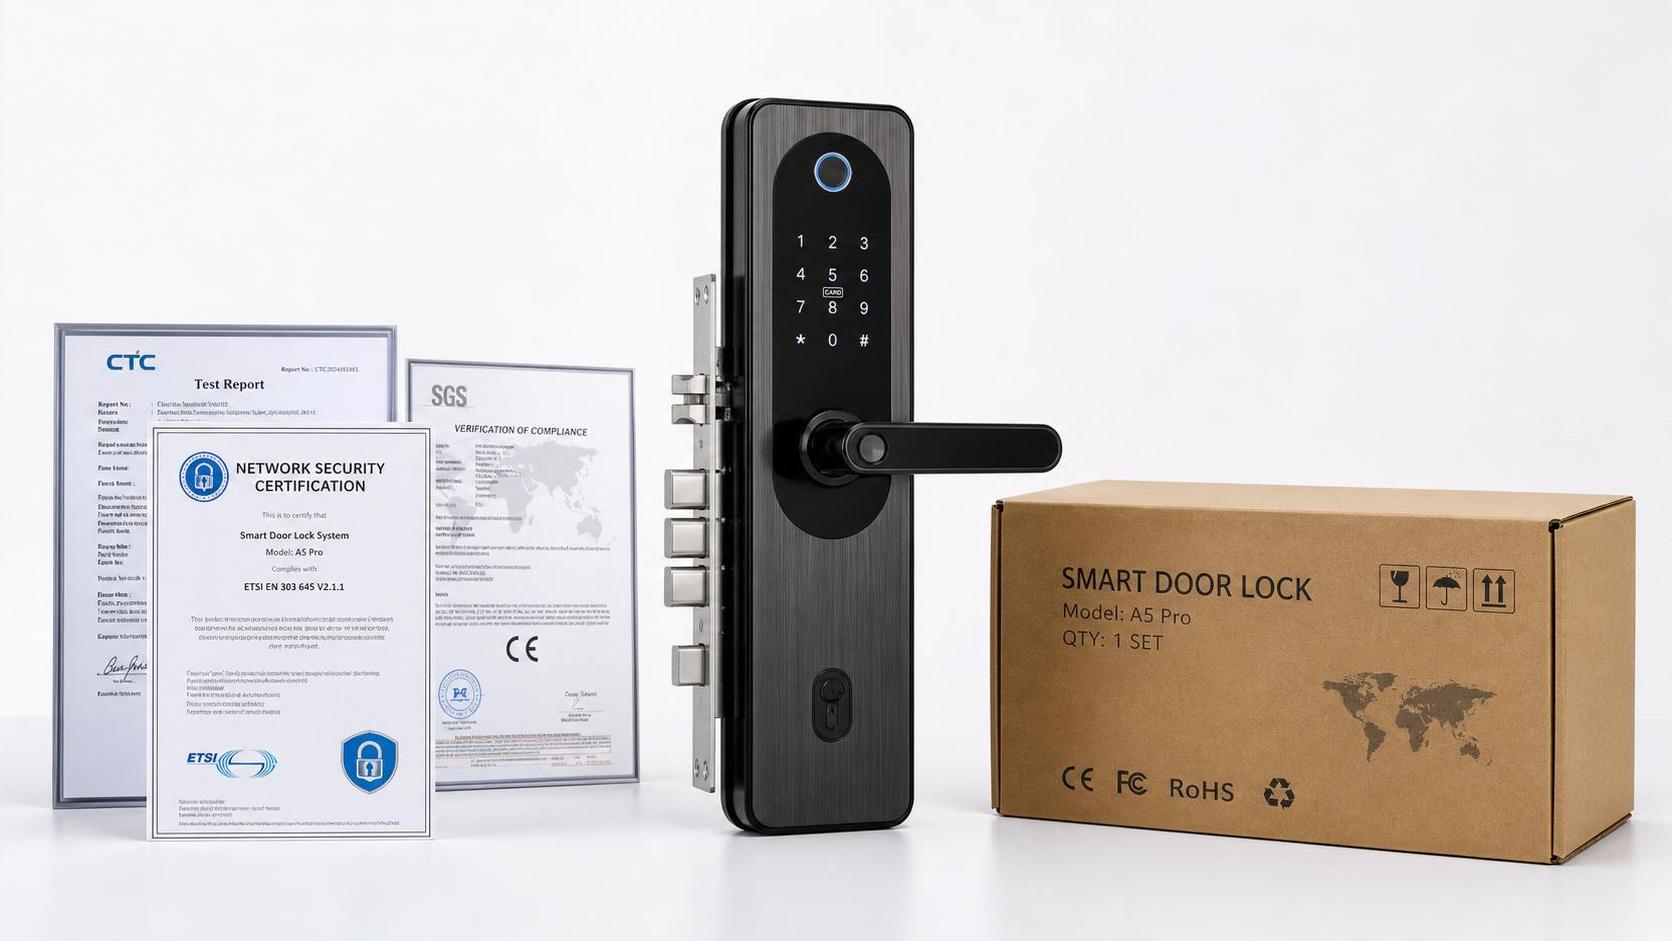
According to the information provided, SASO released the mandatory enforcement notice for SASO IEC 62443-3-3:2026 on July 10, 2026. The notice requires all imported digital locks to obtain industrial cybersecurity grade certification starting on September 15, 2026, and the supporting report must be issued by a laboratory recognized by SASO.
The confirmed scope of impact includes product access to the Saudi market, type-testing timelines, and customs clearance efficiency for affected shipments. The provided information also states that products without the required certification will be refused at Riyadh port.
Where the pressure is likely to appear across the supply chain
Export-facing suppliers will face a stricter entry threshold
From an industry perspective, companies directly exporting digital locks to Saudi Arabia are the first group exposed to the rule change because certification is now tied to whether the product can enter the market at all. The main impact is likely to fall on shipment planning, compliance review, and coordination of testing documents before dispatch.
What deserves closer attention is the gap between existing product readiness and the new certification requirement. Even where a product is already commercially prepared, market entry may still be delayed if the required cybersecurity report from a SASO-recognized laboratory is not in place.
Manufacturing and testing teams may see longer pre-shipment cycles
Observably, the new rule puts pressure on product compliance workflows rather than on sales language alone. For manufacturers and internal compliance teams, the most immediate business effect is likely to be the extension or reshaping of type-testing schedules, because the summary explicitly notes an impact on type-test lead times.
This means the practical issue is not only whether certification is required, but whether production, testing, and shipment windows can still align with customer delivery commitments once the new step is added.
Importers and customs-related operators will need tighter document control
For importers, distributors, and supply chain service providers involved in customs handling, the regulation matters because customs timing and acceptance risk are now connected to cybersecurity compliance evidence. The provided information specifically highlights customs clearance efficiency and the possibility of refusal at Riyadh port for uncertified products.
In operational terms, this increases the importance of document accuracy, submission timing, and upstream coordination with exporters and laboratories before cargo reaches the port stage.
What companies should be checking now
Whether affected products fall within the digital lock scope
Companies serving Saudi-bound orders should first verify which products in their portfolio are treated as digital locks under the new requirement, because the rule is described as applying to all imported digital locks. This is the starting point for deciding which shipments, customers, and orders may be exposed to compliance risk.
Whether laboratory arrangements meet the SASO-recognized requirement
The notice does not stop at requiring certification; it also specifies that the report must come from a laboratory recognized by SASO. In practice, this makes laboratory qualification and report acceptability just as important as the test outcome itself. Businesses should focus on whether their current testing path matches that requirement before relying on existing plans.
Whether delivery schedules still work against the September 15 deadline
Because the rule becomes mandatory on September 15, 2026, shipment timing now matters alongside certification status. Analysis shows that orders close to the enforcement date may require especially careful review, since testing duration, documentation readiness, and customs procedures can affect whether goods move smoothly or encounter delay.
Whether customer and supplier communication is specific enough
Another practical point is communication discipline. Exporters, buyers, contract manufacturers, and logistics partners should align on what certification materials are required, when they must be ready, and how they will be checked before shipment. This is less about broad compliance messaging and more about avoiding mismatches between commercial commitments and actual clearance readiness.
Why this should be read as more than a routine notice
Analysis shows that this development is best understood as an immediate compliance change with broader policy signaling behind it. The immediate result is clear in the provided information: imported digital locks without the required cybersecurity certification face market-access and port-entry risk from September 15, 2026.
At the same time, it is more appropriate to understand this as a longer-term signal that product access requirements are becoming more closely linked to cybersecurity verification, not just conventional product testing. That does not justify assumptions beyond the provided facts, but it does explain why the industry is likely to keep watching how the rule is applied in practice.
How the market should interpret the development now
At this stage, the most reasonable reading is that the Saudi digital lock market is moving from a compliance expectation to a mandatory entry condition tied to recognized cybersecurity certification. The short-term issue is execution: product qualification, report readiness, and customs timing. The broader significance is that cybersecurity documentation is no longer peripheral for affected products entering this market.
It is therefore more appropriate to understand this development as both a near-term operational requirement and a regulatory signal that deserves continued monitoring, especially for businesses with active export schedules or pending Saudi orders.
Basis of this article and what still needs verification
This article is based on the user-provided news title, event date, and event summary. For this type of industry update, relevant source categories typically include official regulatory notices, company announcements, industry association updates, authoritative media reporting, and standard-related documents.
No specific official source link was provided in the input, so the exact original publication channel still requires ongoing verification. What should continue to be monitored includes any further official wording, implementation details, and practical enforcement arrangements related to certification, laboratory recognition, and customs handling.
Industry Briefing
Get the top 5 industry headlines delivered to your inbox every morning.