UL 60730-2-21:2026 Brings Cybersecurity Tests to Built-in Ovens
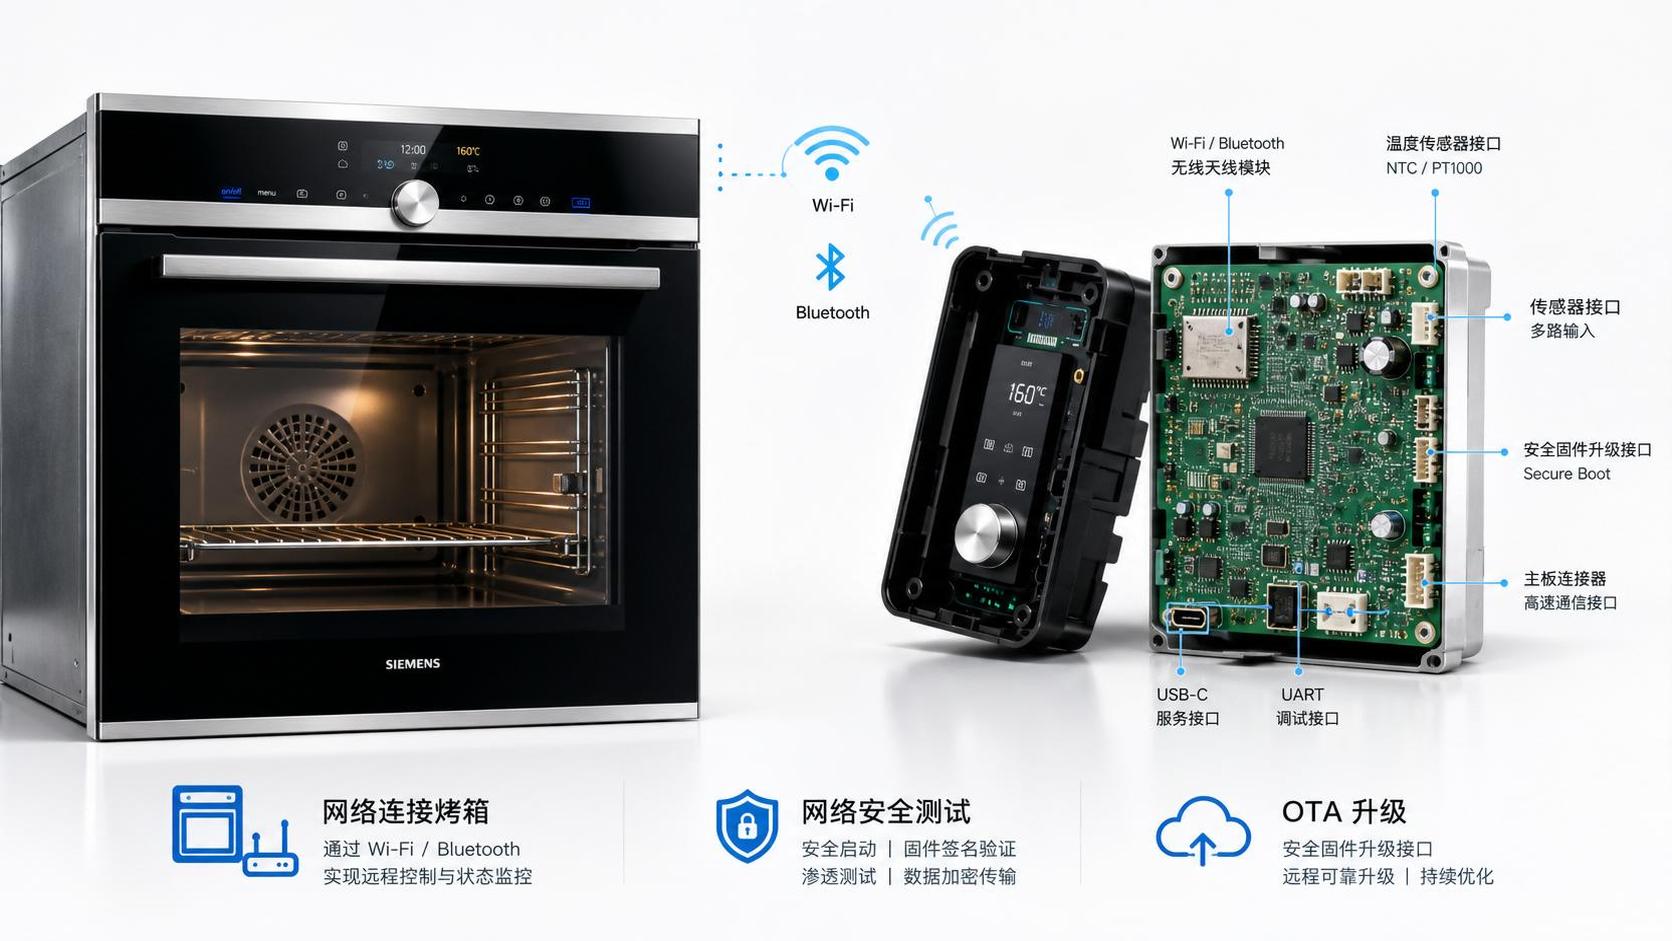
On June 27, 2026, UL issued UL 60730-2-21:2026, bringing Wi-Fi and Bluetooth connected built-in ovens into a mandatory cybersecurity certification scope for the first time. The update is notable not only for appliance brands, but also for control module suppliers, firmware teams, testing providers, importers, and buyers serving the U.S. market, because it links product access more directly to penetration testing and secure update capability rather than treating connectivity as a secondary feature.
What the standard now requires
According to the provided information, UL released UL 60730-2-21:2026 on June 27, 2026. The standard newly places Wi-Fi/Bluetooth connected built-in ovens under mandatory cybersecurity certification requirements. It requires temperature control modules to pass penetration testing based on the OWASP IoT Top 10, and firmware must support secure over-the-air updates (OTA). The standard will become mandatory on January 1, 2027, and UL has already opened a pre-certification channel.
Where the impact is likely to appear first
Connected oven brands and finished-product manufacturers
From an industry perspective, these companies are the most directly affected because the new requirement applies to connected built-in ovens as products entering the market. The main impact is likely to appear in product definition, compliance scheduling, firmware readiness, and model launch timing. What deserves closer attention is whether existing connected models already have the testing and OTA support needed for certification planning before the 2027 effective date.
Temperature control module and electronics suppliers
Analysis shows that suppliers of smart temperature control modules may face earlier technical and documentation demands from appliance manufacturers. The effect is likely to show up in module design review, software security validation, and interface support for secure firmware updates. These suppliers should pay attention to how customers begin translating the UL requirement into procurement specifications and acceptance criteria.
Testing, certification, and compliance service providers
Observably, the opening of a pre-certification channel creates a more immediate workload for labs and compliance service teams. The practical effect may be seen in pre-assessment requests, test preparation, evidence review, and scheduling coordination. These parties should watch for how applicants interpret OWASP IoT Top 10 penetration testing expectations in the context of built-in oven control systems.
Importers, buyers, and channel participants serving the U.S. market
For companies responsible for sourcing or placing connected kitchen appliances into the U.S. market, the change may affect supplier screening, contract requirements, and delivery planning. The issue to monitor is not only whether a product can eventually be certified, but also whether the certification path and supporting firmware capability are aligned with shipment timelines and customer commitments.
What companies should focus on now
Separate confirmed requirements from internal assumptions
The confirmed facts are limited to the new certification scope, the OWASP IoT Top 10 penetration testing requirement, the OTA support requirement, the January 1, 2027 mandatory date, and the existence of a pre-certification channel. Companies should be careful not to treat unconfirmed interpretations as settled compliance rules in internal planning or customer communication.
Check which product lines actually fall within scope
What deserves closer attention is product segmentation. The provided information specifically refers to Wi-Fi/Bluetooth connected built-in ovens. For manufacturers and traders, this means product mapping is an immediate task: identifying which models include the relevant connectivity and which modules are responsible for temperature control functions tied to the new requirement.
Review OTA capability as a deliverable, not a feature claim
Analysis shows that OTA support now matters in a compliance context, not only in a product marketing context. Companies should focus on whether secure remote firmware update capability can be clearly demonstrated, supported in delivery materials, and coordinated across hardware, firmware, and after-sales processes.
Use the pre-certification window to reduce timing risk
Because UL has opened pre-certification before the mandatory date, companies with affected products should pay attention to internal sequencing: design validation, penetration testing preparation, supplier coordination, and customer communication. The main practical question is whether the pre-certification channel can help identify issues early enough to avoid disruption closer to January 2027.
Why this reads as more than a routine update
Observably, this is not just a date change or an editorial revision. The notable point is that cybersecurity testing and secure update capability are being attached directly to a specific connected appliance category within a certification framework. It is more appropriate to understand this as a concrete compliance signal rather than a completed market outcome. The rule is published and the implementation date is defined, but how quickly different companies adapt in product design, sourcing, and certification workflows still needs continued observation.
How this development is best understood now
At this stage, the update is best read as a near-term compliance change with longer-term signaling value. In the short term, it matters because affected products targeting the U.S. market face a defined mandatory date and a clear need for penetration testing and OTA readiness. In the longer view, it suggests that connectivity in household appliances is being evaluated with more explicit cybersecurity expectations. That does not by itself determine market outcomes, but it does raise the importance of security capability in product and supplier decisions.
Basis of this article and follow-up points
This article is based on the user-provided news title, event date, and event summary. For this type of development, relevant source categories usually include official announcements, standard-setting organization documents, company notices, industry association materials, and reporting by established trade media. A specific official source link was not provided in the input, so the exact publication text and any subsequent explanatory materials still need ongoing verification. Follow-up attention should focus on any later official clarifications, implementation guidance, or related testing interpretations tied to UL 60730-2-21:2026.
Industry Briefing
Get the top 5 industry headlines delivered to your inbox every morning.